About Me
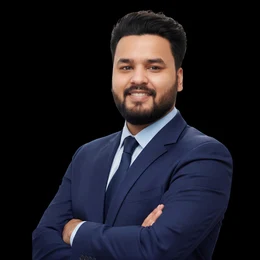
I am a self-taught web developer and security tools specialist based in Bangladesh. I have spent more than 5 years building client-side web applications, and my focus has always been the same: tools that keep your sensitive data on your device, not on a server.
I built 2FA Fast out of a real frustration. Most existing 2FA solutions either required you to have your phone at all times or silently uploaded your authentication secrets to a cloud server, creating a single point of failure. My answer was a fully browser-based TOTP engine built on the Web Crypto API. Your secret key is computed locally and never leaves your browser. That same privacy principle applies to every tool on this site.
My technical work covers PHP 8, vanilla JavaScript, the Web Crypto API, SQLite via PDO, and browser-native security APIs including WebAuthn and the Credential Management API. I have built 18 free security and utility tools covering TOTP generation, QR code generation and decoding, cryptographic hash generation, password strength analysis, Base32 and Base64 encoding, passkey testing, and more. All 18 tools run entirely in your browser with zero server processing of your data.
Through the 2FA Fast blog, I write practical, technically accurate guides on two-factor authentication, TOTP standards (RFC 6238), password security, passkeys, and protecting online accounts. My goal is to make security concepts accessible to both technical and non-technical readers without oversimplifying how things actually work under the hood.
When I am not building security tools, I take on freelance web development projects, primarily working with PHP, JavaScript, and custom CMS solutions for clients across different industries. If you have a tool suggestion, a security question, or just want to say hello, I would love to hear from you.